TIPS Change port 80 GUI

cantVOIP

Member
Joined
Jun 19, 2023
Messages
60
Reaction score
8
I would like to change the GUI port from my IncrediblePBX to anything other than 80. Where can I do this? I can't find port 80 anywhere in the GUI.
I'm running IncrediblePBX2021. I'm a noob, please go easy on me I'm just trying to learn.
 
In more recent IncrediblePBX versions, like the 2021, the web server port is defined in the configuration file :
/etc/apache2/sites-enabled/000-default.conf

You can edit that file with the text editor nano and change the first line which reads <VirtualHost *:80>
The command will be:
nano /etc/apache2/sites-enabled/000-default.conf

Replace 80 with whatever you want. Save the file and restart the PBX.

That said, you might have issues as there may still be some hard-coded http calls inside the scripts which try to connect to port 80. So I am not sure that it's a good idea to replace port 80 with another one.
 
Last edited:
Really good questions. Are you setting up Let's Encrypt TLS?
I think there usedd to be a proprietary module System Admin.
I was going to see if Webmin can be used.
 
Really good questions. Are you setting up Let's Encrypt TLS?
I think there usedd to be a proprietary module System Admin.
I was going to see if Webmin can be used.
There is Certificate Manager, but setting the port in the GUI is a commercial module.

Otherwise it has to be manually set in

(Debian)
/etc/apache2/sites-enabled/000-default.conf
(RHEL)

/etc/httpd/conf/httpd.conf
 
Or you can leave everything almost as is and put a reverse proxy between the world and your server now on 127.0.0.1:80 , the proxy can rewrite http to https and decode using a stock of certs before sending it to 127.0.0.1:80. Also with strict-sni ip or unhandled domains are dropped without leaking domain name on the served cert.
 
Last edited:
Really good questions. Are you setting up Let's Encrypt TLS?
I think there usedd to be a proprietary module System Admin.
I was going to see if Webmin can be used.
That is exactly what I'm doing. I've found some guides on how to do it in FreePBX using the module System Admin, but that module is not included in IncrediblePBX. Have you found a way to make it work?
 
Incredible PBX does not support commercial, non-GPL Sangoma modules.
 
Well, I would agree that it works for good old HTTP-01 with pin holes in your firewall, but that is not 'fine' for me for many reasons ;-)

I want wild card certs , I prefer the security of DNS-01, also for security, I use different certs for different webroots (admin, ucp, fop2 etc.) another for TLS on the extensions and yet another for provisioning but I don't want to touch the opensource FreePBX code.
 
I have to see if the "free" certificates you get from an Oracle CA have a longer expiration date than Let's encrypt.

Or if the CA you get has "a static IP" that can be whitelisted and not leave port 80 open all the time.. I think using Let's Encrypt you have to open port 80 to ANY IP.


What are always free services?
.
.
.

Certificates: 5 Private CA and 150 private TLS certificates

Features and Enhancements included in OCI Certificates

 
Yes, the HTTP-01 protocol generally needs port 80 open to everyone for some particular but well-known URL's and at update times it is undeniably leaky.

DNS-01 doesn't rely on any parts of your web-server or firewall just access to your name service generally with an API key or two, so your PBX box does not even need to be involved at all, this is my choice.

LetsEncrypt issues against HTTP-01 and DNS-01 and wild-card certs requests, the creaky old .php acme client included with FreePBX, not so much.

Most browsers will now reject certs older than 13 months.

These issuers offer 'always free' certs
zerossl.com
letencrypt.org
buypass.com
ssl.com
google.com

there are others
 
Last edited:
Well, I would agree that it works for good old HTTP-01 with pin holes in your firewall, but that is not 'fine' for me for many reasons ;-)

I want wild card certs , I prefer the security of DNS-01, also for security, I use different certs for different webroots (admin, ucp, fop2 etc.) another for TLS on the extensions and yet another for provisioning but I don't want to touch the opensource FreePBX code.


I understand that acme spins up a temp web server on port 80, so firewall seems to still be an issue.
 
No, acme describes methods needed and results to expect , the chosen acme client here is what chooses which recipe/route to use and that is HTTP-01 , I believe this one just suborns the working web-server for it's purpose as only one service can service TCP/80.

As the names suggest, the challenge response for HTTP-01 is over writing then reading http files , DNS-01 does that ping pong directly with dns txt records.
 
Last edited:
I also have an issue just leaving port 80 open to all for the certificate renewal. I rather just my router to generate the certificates automatically every 60 days and manually replacing them in IncrediblePBX. A pain, but better than being exposed.
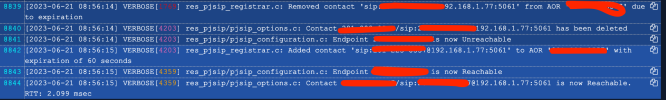
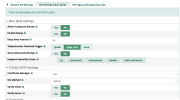
This being said, I uploaded a valid crt and key from let's encrypt to my IncrediblePBX Set it up as default. I switched my pjsip to listen to port 5061. Restarted the entire machine. It seems like my ATA is having issues connecting. Attached is what I see in my logs, it repeats every few minutes. What else needs to be configured for 5061 to work properly between my ATA and PBX. I've also switched the ports in my ATA side.
I am almost certain is a misconfiguration on the PBX side
 

Attachments

  • logs.png
    logs.png
    132.1 KB · Views: 6
  • sip1.png
    sip1.png
    173.4 KB · Views: 6
  • sip2.png
    sip2.png
    146.5 KB · Views: 6
For one thing, the registration on the PBX is expiring before the ATA re-registers. Your example above shows a one second difference between registration expiration and re-register. Reduce the ATA's registration period or increase the PBX expiration for the registration of the ATA. On ATA's I usually have them re-register every 30 seconds.
 
I also have an issue just leaving port 80 open to all for the certificate renewal. I rather just my router to generate the certificates automatically every 60 days and manually replacing them in IncrediblePBX. A pain, but better than being exposed.
This being said, I uploaded a valid crt and key from let's encrypt to my IncrediblePBX Set it up as default. I switched my pjsip to listen to port 5061. Restarted the entire machine. It seems like my ATA is having issues connecting. Attached is what I see in my logs, it repeats every few minutes. What else needs to be configured for 5061 to work properly between my ATA and PBX. I've also switched the ports in my ATA side.
I am almost certain is a misconfiguration on the PBX side


Does this cover your situation?

 
I tried the Acme script, with the DNS API key but couldn't get it to work.

Then I realized that maybe I have to use the Cpanel of the domain hosting.
Interestingly cpanel has DNS-01 option.

Go to cpanel - go to Zone editor. Add "A-record"
pbx.mydomain.com type in the public IP address of your cloud server 123.145.45.45

Then go back to the Cpanel and choose Let's Encrypt - and generate a cert , it will ask you to chooose between HTTP-01 and DNS-01. and you can also get a cert with asterisk for *.mydomain.com or just pbx.mydomain.com

I couldn't get past this point because I don't know how to get hold of the generated cert and private key.
in cpanel you have access to /home/folder not /etc/ssl/certs/ or /etc/ssl/private
acme.sh has a DNS handler for cpanel.


it will put relevant files in .acme/your,domain.name/
and if you had added

--cert-file <file> Path to copy the cert file to after issue/renew..
--key-file <file> Path to copy the key file to after issue/renew.
--ca-file <file> Path to copy the intermediate cert file to after issue/renew.
--fullchain-file <file> Path to copy the fullchain cert file to after issue/renew.
--reloadcmd <command> Command to execute after issue/renew to reload the server.

where file was started with
/etc/asterisk/keys (copy the fullchain to your.domain.name.crt and the key to .key, the reload command should fwconsole certs import and reload your webserver, then you should be good to go and bypass the FreePBX certificate manager which you should disable when you get it working.
 
Last edited:
Get 3CX - Absolutely Free!

Link up your team and customers Phone System Live Chat Video Conferencing

Hosted or Self-managed. Up to 10 users free forever. No credit card. Try risk free.

3CX
A 3CX Account with that email already exists. You will be redirected to the Customer Portal to sign in or reset your password if you've forgotten it.
Back
Top